
Trust the CMMC experts.
We are a certified, specialized cybersecurity compliance service provider with a long track record of helping our customers with NIST SP 800-171, DFARS and CMMC 2.0 beginning-to-end cybersecurity services and solutions.
We will tell you exactly what you need.
Then, we'll deliver it. All of it.
CyberSheath's partnership approach allowed us to stay focused on delivering quality design services while they expertly guided us through the complexities of compliance. Achieving CMMC compliance gives us confidence to pursue future DOD contracts knowing our security foundation is solid and has positioned us for long-term success.
Chris Brown, SVP, Director – Federal,
Barge Design Solutions
CyberSheath came on at a time when we were very vulnerable and brought us to the finish line. They show you exactly what they're doing, what they're tracking, and what controls are in place. That transparency made all the difference for us. Without them, we would not have been able to meet compliance requirements as quickly as we did.
Megan Downie, VP of Technology and Corporate Operations,
Spirit Electronics
CyberSheath approached this as a strategic partnership, not just a compliance checklist. They took the time to understand how our consultants operate, where CUI truly intersects with our systems and how to protect it without disrupting our core mission.
Mary Corcoran, Chief Administrative Officer,
Tunnell Government Services
We’re CMMC/DFARS experts.
We helped write the rules.
We’ll help you follow them.
Our executives have been involved in the development of every major cybersecurity initiative since 2008.
We have completed hundreds of NIST 800-171
assessments and implementations for our clients, and we are a certified CMMC 2.0 Level 2 service provider.

Expertise. Experience. Results.

1,000s

Level 2 Certified

100%

25%

99%

78+

We solve the whole problem.
We are one of the industry’s few one-stop providers.
We apply our three-stage AIMTM process —
Assess, Implement, Manage — to achieve and
maintain full compliance with all applicable DOD
requirements, at the appropriate level, with a
minimum amount of pain.


It’s about compliance.
Not just software.
Be careful when talking to
software-first providers.
Selling Microsoft GCC licenses is how
many value-added resellers (VARs)
make their money, which can increase
your chance of overpaying to under-
comply. How do you identify a software-
first provider?


Get CMMC 2.0 compliant.
CMMC 2.0 noncompliance is a deal breaker for DOD contracts.
The DOD is now including CMMC 2.0 compliance requirements in the vast majority of RFIs, RFQs, RFPs, and contracts. Protect your business and your employees. Get compliant.
Federal Enclave: Achieve compliance without rebuilding your entire environment.
For organizations that support both DOD and commercial customers, CyberSheath’s Federal Enclave provides a purpose-built, cloud-based compliant environment to securely handle DOD project data. Designed to meet NIST SP 800-171, DFARS and CMMC 2.0 requirements, it enables contractors to isolate Controlled Unclassified Information without overhauling legacy infrastructure. The enclave can be deployed rapidly, helping organizations maintain eligibility for new contract awards, recompetes, and extension years.

Information. Insights. Knowledge.
Case Studies
Read stories about how your peers are achieving CMMC Level 2 compliance with CyberSheath support.
Browse Here >
Education Services
Education Services LLC is a small business specializing in custom training development and learning platforms for defense and technology companies. The company brings expertise in learning science, instructional design, curriculum development, competency assessment, and user…
Learn MoreWebinars
Learn from CyberSheath experts about how to get CMMC compliant and avoid the pitfalls.
Browse Here >
DIBCAC Assessment: No Tricks, No Treats, Just the Facts
For defense contractors, demonstrating implementation of NIST SP 800-171 requires more than having policies and security controls in place. Your documentation, evidence, and actual practices should align and demonstrate that the security requirements described in…
Learn MoreBlogs
Gain useful insights and information on the processes and challenges of CMMC compliance.
Browse Here >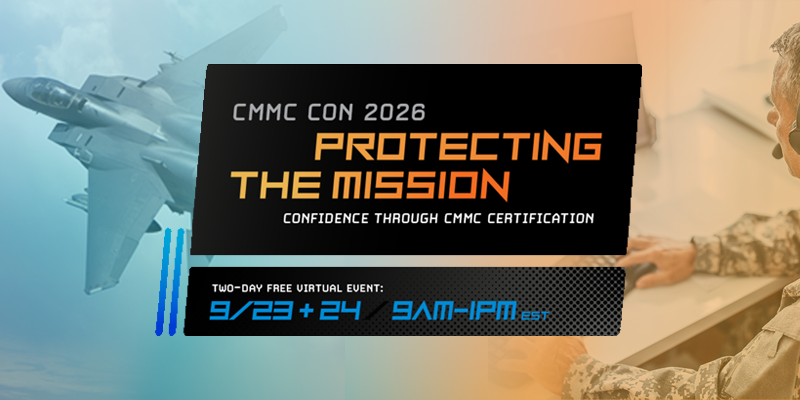
Takeaways from CMMC CON 2026: Protecting the Mission
The Pentagon’s pause of CMMC Phase 2 rocked the defense industrial base (DIB). Some contractors interpreted “pause” as permission to stop. At CMMC CON 2026, speakers from across the DIB, the Pentagon, and the legal…
Learn MoreEvery solution begins with a conversation.
Contact our experts today for a no-obligation discussion of CMMC 2.0 compliance, what’s required, what you may need and what we can do to provide it. We’ve helped hundreds of DOD contractors. We can help you.
